A workable jobsite security plan starts with owned workflows
A practical construction IT checklist for securing field laptops, cloud project files, subcontractor access, jobsite networks and recovery.
Test the plan against a lost-device and mailbox scenario
Assume a superintendent's laptop is stolen while the user's mailbox sends unusual sharing invitations. Walk through reporting, identity verification, session revocation, device-management actions, sharing review, evidence handling and replacement access. Confirm an authorized person can reach the current approved files without restoring the suspect device, then assign owners and dates to every gap.
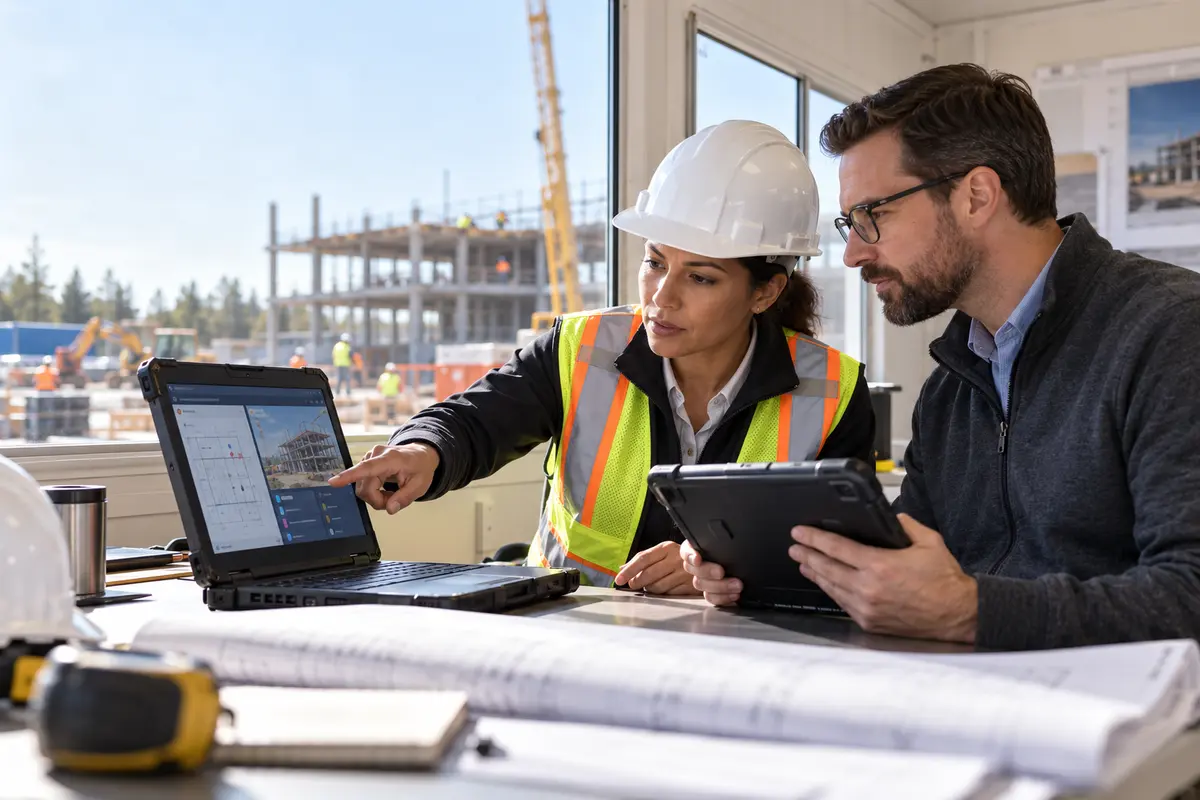
A construction company rarely operates from one controlled office. Estimators may work at headquarters, project managers move between jobs, superintendents use tablets in temporary trailers, and subcontractors need selected documents for a limited time. The security plan has to follow that real workflow without making the field team invent workarounds.
The goal is not to lock down every device in the same way. It is to know which project information is authoritative, which people and devices may reach it, who watches for trouble, and how the business will keep working if a laptop is lost, an account is compromised or a cloud folder becomes unavailable.
Map the job before choosing controls
Start with one active project and follow information from bid through closeout. Include drawings, specifications, requests for information, submittals, schedules, photographs, time records, change orders, invoices and project correspondence. For each step, identify the approved application or folder, its business owner, the users who need access, and the device and connection they use.
This exercise often reveals two different problems: the company does not have a clear source of truth, or the right source exists but people cannot reliably reach it. Security tools cannot settle which drawing revision is approved. That decision belongs to the authorized project team; IT should make the approved location usable, controlled and recoverable.
| Workflow | Questions to answer | Useful evidence |
|---|---|---|
| Plans and field documents | Where is the approved set? Who may change, download or share it? | Site owner, permission groups, version history and closeout procedure |
| Field devices | Which laptops, tablets and phones are supported? What happens when one is lost? | Inventory, assigned user, encryption and management status, last check-in |
| Subcontractor access | Which project and role require access? Who approves it and when should it end? | Named guest, sponsor, scope, review date and removal record |
| Temporary site network | Who owns the router and wireless configuration? Which devices share the network? | Provider details, equipment list, network diagram and support contact |
| Recovery and closeout | What must be restored, retained or handed over? Who validates the result? | Recovery test, archive owner, retention decision and acceptance record |
Set a standard for company and personal devices
Decide which field tasks require a company-managed device and whether personally owned phones or tablets may access business information. The answer can vary by workflow. A supervisor may need a managed tablet with offline files and camera access, while a subcontractor may only need browser access to a selected folder.
The NIST mobile device security guidance covers organization-provided and personally owned devices across deployment, use and disposal. For a construction firm, translate that lifecycle into an operating checklist: approved models and operating systems, enrollment before issue, encryption, screen lock, supported applications, security updates, inventory, incident reporting, data removal and documented retirement.
Centralized device management can enforce selected settings and help administrators see whether a device still checks in. It does not replace a process for assigning equipment, recovering it from a departing employee, or deciding what company information may be stored locally. Define those responsibilities before deploying a tool.
Protect identities before project folders
Use an individual account for each employee and external collaborator. Shared foreman or trailer accounts make it difficult to remove one person's access or understand who changed a file. Require multifactor authentication for supported business systems, protect administrative accounts separately, and keep a recovery route that does not depend on a single person's phone or mailbox.
Group access by project and role instead of granting it one folder at a time whenever possible. An estimator, superintendent, accounting employee and subcontractor usually need different capabilities. The project owner should approve membership; IT should implement and report on it. Neither side should assume the other approved a person merely because the request arrived by email.
The NIST Cybersecurity Framework 2.0 Small Business Quick-Start Guide treats cybersecurity as risk management, not a product list. Its Govern, Identify, Protect, Detect, Respond and Recover outcomes are a useful check: access controls are incomplete if nobody reviews them, detects misuse or owns the response.
Make external sharing deliberate and reversible
Construction collaboration often requires external access, but not every project folder should use the same sharing setting. Separate internal business records from spaces intended for owners, architects, engineers, vendors or subcontractors. Prefer named, authenticated access when the workflow supports it, grant only the required role, and record a sponsor and review date.
Microsoft's current SharePoint and OneDrive external-sharing overview explains that sharing is controlled at both organization and site levels, with the more restrictive setting applying. It also recommends permissions planning and notes that access can be stopped by removing guest permissions or deleting an anyone link. If your team uses Microsoft 365, review the actual tenant and site configuration rather than relying on a remembered default.
At project closeout, export or retain material according to the business's contractual and records decisions, confirm who owns the archive, and remove access that is no longer required. Closing the trailer but leaving guest accounts, shared links and temporary subscriptions active is not a technical handover.
Build temporary networks like business infrastructure
A jobsite connection may begin as a cellular hotspot and grow into a trailer network with printers, cameras, access control, personal phones and vendor equipment. Document the internet provider, router, wireless access points, administrator, configuration backup and fault contact. Confirm coverage and capacity with real workflows before a major mobilization.
Separate business devices from guest and untrusted equipment where the design supports it. Change vendor defaults, keep network equipment supported and updated, and control remote administration. Do not connect specialist safety, surveying, building-control or machine systems to a business network without the equipment owner and qualified vendor confirming the arrangement.
Plan teardown while planning setup. Record who collects the router, cancels service, removes temporary accounts and preserves any required configuration or records. Otherwise, a network built for a six-month project can become an unmanaged service nobody remembers paying for.
Connect endpoint monitoring to a response owner
Endpoint protection, EDR or an MDR service may provide evidence when a field laptop runs suspicious software, an account behaves unusually or a malicious action is blocked. The useful question is what happens next. Define who reviews the alert, who can isolate the device, who contacts the user, and who may accept an interruption to a project-critical workstation.
An alert is not automatically proof of a breach, and a blocked event is not automatically the end of an investigation. Identity, email, firewall and cloud audit information may be needed to understand scope. A managed endpoint detection and response arrangement should specify coverage hours, supported devices, escalation routes and the authority to act.
Back up the project outcome, not only a server
Identify where project records actually live: a file server, Microsoft 365, a construction management platform, staff laptops, email, a finance system or several of these. Ask each provider what is retained, for how long, and how a usable restore is requested. Version history, platform availability, an archive and an independent backup solve different problems.
Set recovery priorities around work. If the primary project manager's laptop fails, can another authorized person reach the current documents and communications? If a folder is deleted or encrypted, what recovery point and restore time does the business need? If a cloud application is unavailable, which minimum records allow the team to make the next safe and authorized decision?
Test a representative recovery before closeout. Restore a selected project folder or supported system to a controlled location, have an authorized project owner verify the result, and record the time, missing dependencies and updated instructions. Genius Fixers can help scope backup and disaster recovery around those recovery outcomes.
Make crew changes a repeatable IT event
For each employee, consultant or subcontractor, record the approver, project, role, device, licenses and intended end date. Prepare accounts and equipment before the start date, then confirm access with the actual job task. At departure or project completion, disable access, recover company equipment, transfer owned records and review forwarding or mailbox needs under the company's policy.
Temporary does not mean informal. A short engagement can still expose bid details, contact information, drawings or financial instructions. A repeatable onboarding and offboarding process reduces the chance that urgency turns into broad permanent access.
Run one realistic field incident exercise
Assume a superintendent reports that a laptop was taken from a vehicle and the user's mailbox is sending unusual sharing invitations. Walk through the first hour: who receives the report, who verifies the caller, who disables sessions, who evaluates remote lock or wipe, who reviews project sharing, who preserves relevant evidence, and who decides whether owners, vendors or insurers must be contacted.
Then test continuity. Can an authorized replacement device reach the approved drawings and schedule without restoring the suspect laptop? Can the team identify the most recent legitimate file change? Does the incident contact list work when email is part of the problem? Record gaps as assigned actions with dates, not as general lessons.
A practical 30-day starting plan
- Week 1: choose one project. Map its people, devices, applications, external parties and authoritative records.
- Week 2: reconcile access and assets. Confirm named accounts, multifactor authentication, device ownership, project groups and guest sponsors.
- Week 3: check operations. Review network ownership, endpoint alert routing, update status, backup scope and closeout tasks.
- Week 4: test and assign. Run the lost-device scenario, restore representative data, and assign each gap to a business or technical owner.
This limited review produces evidence the company can use. It is more useful than buying a broad security bundle before anyone knows which jobsite workflow it must protect.
Frequently asked questions
Should construction workers use personal phones for project files?
Only under a deliberate policy. Decide which tasks and information are allowed, what authentication is required, whether the device must be managed, how business data is separated or removed, and what support the company will provide. Some workflows may require company-managed devices; others may allow restricted browser access.
Can subcontractors have access to only one project?
Usually, if the collaboration platform and folder design support project-based permissions. Use named accounts or guests, a project sponsor, the minimum required role and a review or end date. Test access as the subcontractor experiences it and confirm that unrelated projects are not visible.
Is a cloud construction platform already backed up?
The provider may offer resilience, retention, versioning or exports, but those features do not automatically meet every recovery requirement. Review the current contract and documentation, decide which loss scenarios matter, and test how an authorized person recovers a representative record.
What should happen when a jobsite laptop is lost?
The user should report it through a known channel immediately. The response owner can verify the incident, evaluate account sessions and device-management actions, review sensitive local or cloud access, preserve appropriate evidence and arrange a replacement workflow. The exact steps depend on the device's configuration and the information involved.
Can an IT provider manage both the office and jobsite environment?
Yes, when the scope clearly identifies supported users, devices, networks, applications, locations, hours and vendor boundaries. Specialist construction, safety and operational equipment may require its manufacturer or another qualified provider. Genius Fixers offers remote assistance and scheduled on-site business IT support across Virginia, Maryland and Washington, DC, subject to confirmed availability and project requirements.
Connect office and field IT around the same plan
Genius Fixers can review your construction company's field devices, project access, jobsite connectivity, endpoint monitoring and recovery responsibilities. We provide remote support and scheduled on-site business IT across Virginia, Maryland and Washington, DC, with scope and travel confirmed for each engagement.
Book a free phone or Zoom consultation
Explore IT support for construction and contracting teams, or call 703-419-9000.